Drop Down MenusCSS Drop Down MenuPure CSS Dropdown Menu
Alternative Text Alternative Text Alternative Text Alternative Text
Survivor of US Drone Attack:
Obama Belongs on List of World's Tyrants

Poisoning Black Cities: Corporate Campaign to Ethnically Cleanse US Cities Massive Marches in Poland
Against Authoritarian Threat of Far-Right
Ethiopia’s Invisible Crisis: Land Rights Activists Kidnapped and Tortured

Global Perspectives Now Global Perspectives Now
Showing posts with label Edward Snowden. Show all posts

Is This the REAL Apple Corporation?: iPhone Has Secret Software — Can be Remotely Activated to Spy on People Says NSA Whistle Blower

iPhoneBy Andrew Griffin
The iPhone has secret spyware that lets governments watch users without their knowledge, according to Edward Snowden.

The NSA whistleblower doesn’t use a phone because of the secret software, which Snowden’s lawyer says can be remotely activated to watch the user.

"Edward never uses an iPhone, he’s got a simple phone," Anatoly Kucherena told Russian news agency RIA Novosti. "The iPhone has special software that can activate itself without the owner having to press a button and gather information about him, that’s why on security grounds he refused to have this phone."

Read More


NSA Whistleblower's Documents Reveal Encryption Standards the NSA 'Can't Crack'

Illustration provided by Chris Dlugosz.


By Dhananjay Harkare
National Security Agency also known as NSA, the US intelligence agency has been a hot topic of discussion after former member Edward Snowden revealed its dark side. An archive of Snowden’s documents suggests the encryption schemes that NSA can break easily along with those it can’t crack. The reports suggest that by 2012, NSA couldn't decrypt few emails and chats which were encrypted with right algorithms. The information about documents is shared by Der Spiegel which informs about NSA’s encryption-breaking programs and few standards that are troublesome for the agency.

[...]

For NSA, a combination of Tor, strongly implemented encryption standard, messaging system CSpace and a system for VoIP called ZRTP becomes catastrophe. Also Pretty Good Privacy aka PGP, used to documents and emails is unbreakable for NSA. The findings based on these documents were earlier presented on-stage by researchers. It would now be interesting to see if Edward Snowden has anything to say on this. We will keep you updated on that front.

Read More

Local Police Forces Have Morphed Into the Natioan Security Agency: Police Agencies In Virginia Quietly Stockpiling Private Phone Records

All over the U.S., local police agencies are collecting vast stockpiles of private information from people – some of it from people who have not been convicted of crimes but were merely stopped by police.

From Electronic Frontier Foundation.
By G.W. Schulz
While revelations from Edward Snowden about the National Security Agency’s massive database of phone records have sparked a national debate about its constitutionality, another secretive database has gone largely unnoticed and without scrutiny.

The database, which affects unknown numbers of people, contains phone records that at least five police agencies in southeast Virginia have been collecting since 2012 and sharing with one another with little oversight. Some of the data appears to have been obtained by police from telecoms using only a subpoena, rather than a court order or probable-cause warrant. Other information in the database comes from mobile phones seized from suspects during an arrest.

The five cities participating in the program, known as the Hampton Roads Telephone Analysis Sharing Network, are Hampton, Newport News, Norfolk, Chesapeake and Suffolk, according to the memorandum of understanding that established the database. The effort is being led in part by the Peninsula Narcotics Enforcement Task Force, which is responsible for a “telephone analysis room” in the city of Hampton, where the database is maintained.

The unusual and secretive database contains telecom customer subscriber information; records about individual phone calls, such as the numbers dialed, the time the calls were made and their duration; as well as the contents of seized mobile devices. The information is collected and shared among police agencies to enhance analysis and law enforcement intelligence.

The legality of the database is in question, however, and at least one law enforcement agency has declined to participate in the program due to such concerns.

“My initial reaction is that it's very disturbing and illegal under Virginia law,” said Rob Poggenklass, a staff attorney at the American Civil Liberties Union of Virginia, which was previously unaware of the database.

The system was set up with virtually no public debate or concern expressed by elected officials, who approved resolutions authorizing the database. Hardly anyone outside of the five participating police agencies knows about the sharing network, though its creation was not kept secret.

All over the U.S., local police agencies are collecting vast stockpiles of private information from people – some of it from people who have not been convicted of crimes but were merely stopped by police.

As an example of the amount of data being collected, in the first-ever transparency reports released by major telecoms earlier this year, AT&T revealed that between January and June, it received nearly 80,000 criminal subpoenas for customer records from federal, state and local law enforcement agencies, while Verizon disclosed that it had received over 72,000 subpoenas from law enforcement during the same period.

The Virginia system is yet another example of this creeping expansion of local law enforcement surveillance throughout the country.

Minimal public information about the sharing network exists, but it first made an appearance on the agendas of local government meetings, where it met no resistance. Elected city council members in Newport News and Chesapeake, for instance, passed resolutions approving the telephone data-sharing agreement without objection.

Read More


New Zealand Cops Raided Home of Reporter Working on Snowden Documents

Nicky Hager. (Screen capture from YouTube video)
By Glenn Greenwald and Ryan Gallagher
Agents from New Zealand’s national police force ransacked the home of a prominent independent journalist earlier this month who was collaborating with The Intercept on stories from the NSA archive furnished by Edward Snowden. The stated purpose of the 10-hour police raid was to identify the source for allegations that the reporter, Nicky Hager, recently published in a book that caused a major political firestorm and led to the resignation of a top government minister.

But in seizing all the paper files and electronic devices in Hager’s home, the authorities may have also taken source material concerning other unrelated stories that Hager was pursuing. Recognizing the severity of the threat posed to press freedoms from this raid, the Freedom of the Press Foundation today announced a global campaign to raise funds for Hager’s legal defense.

In August, one month before New Zealand’s national election, Hager published Dirty Politics, which showed that key figures in Prime Minister John Key’s National Party were feeding derogatory information about their opponents to a virulent right-wing blogger named Cameron Slater. Hager published evidence in the form of incriminating emails, provided by a hacker, demonstrating coordination between National Party officials and Slater. The ensuing scandal forced the resignation of a top Key ally, Justice Minister Judith Collins, and implicated numerous other National Party officials and supporters. Despite the scandal, the National Party won a resounding victory in the election, sending Key to a third term as prime minister.

On October 2—less than two weeks after the election—detectives from a regional “major crime team” came to Hager’s Wellington home armed with a search warrant authorizing them to seize anything that might lead them to the identity of his source for Dirty Politics. The warrant shows that prior to the raid, a police “intelligence analyst” had studied Hager’s media appearances in an effort to discover information about his sources for the book, taking particular note of references Hager made to knowing the source’s identity.

Read More

The Internet Has A 'Shut Off Button': The NSA Caused Web Blackout in Syria, Not the Syrian Government — Says NSA Whistleblower


By Spencer Ackerman
The surveillance whistleblower Edward Snowden has alleged that a 2012 incident that took Syria’s internet offline was caused by a National Security Agency blunder.

In an interview with Wired magazine, Snowden said the elite NSA hacking unit, called Tailored Access Operations, accidentally cut off Syria’s internet while attempting to infiltrate it.

The unit allegedly attempted to install an exploit in the hardware of Syria’s main internet service provider that would have provided NSA with mass access to internet usage, communications and patterns in Syria, where a civil war was developing into an Islamist insurgency, destabilising the Middle East.

Instead of gaining mass visibility into the internet habits of Syrians, Snowden alleged, a glitch took Syria offline.

On 29 November 2012, the analysis firm Renesys reported that 92% of the routed networks providing internet connectivity for Syria, 77 of them, had gone dark.

At the time, the outage was widely reported, including by the Guardian, to have been at the instigation of the Syrian government, in order to destabilise opposition groups.

Read More


Israel Flagged as Top Security Threat to US - According to New NSA Whistleblower Document

Israel is considered a 'leading threat' to the infrastructure of US financial and banking institutions, and a threat in the development of weapons of mass destruction.

Photo by brionv.
By Jeff Stein
Israel was singled out in 2007 as a top espionage threat against the U.S. government, including its intelligence services, in a newly published National Security Agency (NSA) document obtained by fugitive leaker Edward Snowden, according to a news report Monday.

The document also identified Israel, along with North Korea, Cuba and India, as a “leading threat” to the infrastructure of U.S. financial and banking institutions.


The threats were listed in the NSA’s 2007 Strategic Mission List, according to the document obtained by journalist/activist Glenn Greenwald, a founding editor of The Intercept, an online magazine that has a close relationship with Snowden, a former NSA and CIA contractor who fled the U.S. with thousands of top-secret documents last year.

In this new document, Israel was identified by the NSA as a security threat in several areas, including “the threat of development of weapons of mass destruction” and “delivery methods (particularly ballistic and nuclear-capable cruise missiles).” The NSA also flagged Israel’s “WMD and missile proliferation activities” and “cruise missiles” as threats.

Read More

NSA's 'Looking for Foreign Terrorist' Excuse for Spying On Americans Falls Apart: 90% of Intercepted Conversations Were Not 'Intended Surveillance Targets'

(Illustration by EFF)
By Mohammad Zargham; Editing by Lisa Shumaker
The Washington Post said on Saturday a study of a large collection of communications intercepted by the U.S. National Security Agency showed that ordinary Internet users, including Americans, far outnumbered legally targeted foreigners caught in the surveillance.

"Nine of 10 account holders found in a large cache of intercepted conversations, which former NSA contractor Edward Snowden provided in full to The Post, were not the intended surveillance targets but were caught in a net the agency had cast for somebody else," the Post said.

Nearly half of the files "contained names, email addresses or other details that the NSA marked as belonging to U.S. citizens or residents," it said.

Read More

Is Glenn Greenwald's New 'Independent Investigative' News Corp A Myth?: Story 'Delayed' After Complaints From US Government

Glenn Greenwald.
Glenn Greenwald. (Photo by Gage Skidmore)
By Donn Marten
On Monday, Pulitzer prize winning journalist Glenn Greenwald let the news slip via Twitter that his long-awaited NSA story was to be published on The Intercept at midnight. By Tuesday morning, much to the dismay of myself and many others it appeared that the site - which since its rollout has been disappointly devoid of new material - has caved to government pressure tactics and did not post the story.

According to a rather cryptic Tweet by Greenwald later on Monday, "After 3 months working on our story, USG today suddenly began making new last-minute claims which we intend to investigate before publishing". Might any of those claims be based on trumped up charges that publication would play right into the hands of the "terrorists" and could a permanent delay be in the works?


While I have remained a skeptic to the allegations that the new First Look Media venture that lured Greenwald with the siren song of creating a new and uncompromising investigative journalism forum that was an alternative to the entrenched corrupt state-corporate media the pulling of the big story only serves to bolster them. When you throw in with the billionaire wolves you will sooner or later being devoured and EBay founder Pierre Omidyar's agenda has already been found by some, for example journalist Chris Floyd to be suspect with support to both the coup government in Kiev as well as the right-wing regime of the newly elected Narendra Modi of India. The problem is that at the end of the day all of these one-percenter elite pigs stick together and Greenwald should have been far more judicious in his association with one of them.

It would have been a brilliant touch were the story of NSA surveillance of domestic political dissidents and well known figures were to have broken during the week of the orgy of flag-sucking excess that is the Fourth of July and Greenwald may have ill-advisedly tipped his hand during that interview with GQ "The Man Who Knows Too Much" when he alluded to fireworks:

I think we will end the big stories in about three months or so [June or July 2014]. I like to think of it as a fireworks show: You want to save your best for last. There's a story that from the beginning I thought would be our biggest, and I'm saving that. The last one is the one where the sky is all covered in spectacular multicolored hues. This will be the finale, a big missing piece. Snowden knows about it and is excited about it.

For now at least the fireworks show has been postponed.

Read More


Google Had Close Relationship With the NSA: Emails Show Google Executives and NSA 'Coordinated' On A Variety of Issues

Eric Schmidt, executive chairman of Google. (Photo by
Charles Haynes
)

By Jason Leopold
Email exchanges between National Security Agency Director Gen. Keith Alexander and Google executives Sergey Brin and Eric Schmidt suggest a far cozier working relationship between some tech firms and the U.S. government than was implied by Silicon Valley brass after last year’s revelations about NSA spying.


Disclosures by former NSA contractor Edward Snowden about the agency’s vast capability for spying on Americans’ electronic communications prompted a number of tech executives whose firms cooperated with the government to insist they had done so only when compelled by a court of law.

But Al Jazeera has obtained two sets of email communications dating from a year before Snowden became a household name that suggest not all cooperation was under pressure.

On the morning of June 28, 2012, an email from Alexander invited Schmidt to attend a four-hour-long “classified threat briefing” on Aug. 8 at a “secure facility in proximity to the San Jose, CA airport.”

“The meeting discussion will be topic-specific, and decision-oriented, with a focus on Mobility Threats and Security,” Alexander wrote in the email, obtained under a Freedom of Information Act (FOIA) request, the first of dozens of communications between the NSA chief and Silicon Valley executives that the agency plans to turn over.

Read More

Glenn Greenwald to Publish Names of Americans NSA Spied On — Calls it a 'The finale, a Big Missing Piece'

Illustration by Marcus Brown
Illustration by Marcus Brown.

By Alyssa Figueroa
Those who have grown apathetic about the National Security Agency violating privacy rights, may soon find their interest renewed, as the political is about to get very personal. According to The Sunday Times of London, Glenn Greenwald will publish the names of Americans targeted by the NSA.


“One of the big questions when it comes to domestic spying is, ‘Who have been the NSA’s specific targets?’” he told the Times. “Are they political critics and dissidents and activists? Are they genuinely people we’d regard as terrorists? What are the metrics and calculations that go into choosing those targets and what is done with the surveillance that is conducted? Those are the kinds of questions that I want to still answer.”

Greenwald has promised that this will be the “biggest” revelation of the nearly two million classified files he received from Edward Snowden, and that “Snowden’s legacy would be ‘shaped in large part’ by this ‘finishing piece’ still to come."

"I think we will end the big stories in about three months or so [June or July 2014]. I like to think of it as a fireworks show: You want to save your best for last."

Read More

NSA Mass Spying — Nothing Has Changed Since the Snowden Revelations: 'Can the Surveillance State Be Stopped?'

"It's okay honey, Congress says they're heroes" (Illustration by EFF)
American officials won't confront NSA's domestic spying because they're afraid it
might have information about their own illegal doings. (Illustration by EFF)
Despite the public furor over NSA whistleblower Edward Snowden’s revelations about U.S. government surveillance, the process rolls on unabated with few prospects of significant reform.


By Danny Schechter
With the publication of Glenn Greenwald’s new book on Edward Snowden and the National Security Agency, the state surveillance issue is back in full force, as if it ever went a way.

Purloined formerly top-secret NSA documents are now there for the downloading, even as the calls for truth and privacy buttressed by irrefutable information, has run up against the institutional armor of the surveillance state that has little respect for public opinion or calls for “reform.”

Every day, there are new stories showing duplicity in high places and revealing the existence of new tracking technologies and forced and voluntary collusion between the secret agency and its many “partners” in the private sector. PBS “Frontline” is out with one more exposé.

Just as the publication of the Pentagon Papers in l971 did not end the Vietnam War, the leaks from a world of questionable “intelligence” gathering have only made our spymasters more determined. There were more years of carnage after Daniel Ellsberg dropped the hidden history of our intervention in Vietnam showing how officials knew the truth even as they fed the public a litany of lies to keep a profitable if murderous enterprise going.

The charade was finally ended by the Vietnamese liberation army 39 years ago, but the NSA and its handsomely financed partners in the self-styled “Intelligence Community” will go on and on until someone stops them and their spying, and that someone is hard to identify given the way the agencies seem to have the goods on the government as well as the rest of us.

There is no American liberation army with the clout to shut them down.

I spoke with retired CIA veteran Ray McGovern for a TV series I am producing about how government spying intimidates people in government. He told me:

“Everybody is afraid. It’s not just the journalists, it’s people like Barack Obama, it’s people like Dianne Feinstein – think about what the NSA has on Dianne Feinstein and her husband who has made billions from defense and post office and all kinds of nice cozy contracts, okay? This goes back to J. Edgar Hoover…”

Read More


Everyone Should Know Just How Much The Government Lied To Defend The NSA

Photo by Tony Fischer.
A web of deception has finally been untangled: the Justice Department got the US supreme court to dismiss a case that could have curtailed the NSA's dragnet. Why?


By
If you blinked this week, you might have missed the news: two Senators accused the Justice Department of lying about NSA warrantless surveillance to the US supreme court last year, and those falsehoods all but ensured that mass spying on Americans would continue. But hardly anyone seems to care – least of all those who lied and who should have already come forward with the truth.

Here's what happened: just before Edward Snowden became a household name, the ACLU argued before the supreme court that the Fisa Amendments Act – one of the two main laws used by the NSA to conduct mass surveillance – was unconstitutional.

In a sharply divided opinion, the supreme court ruled, 5-4, that the case should be dismissed because the plaintiffs didn't have "standing" – in other words, that the ACLU couldn't prove with near-certainty that their clients, which included journalists and human rights advocates, were targets of surveillance, so they couldn't challenge the law. As the New York Times noted this week, the court relied on two claims by the Justice Department to support their ruling: 1) that the NSA would only get the content of Americans' communications without a warrant when they are targeting a foreigner abroad for surveillance, and 2) that the Justice Department would notify criminal defendants who have been spied on under the Fisa Amendments Act, so there exists some way to challenge the law in court.

It turns out that neither of those statements were true – but it took Snowden's historic whistleblowing to prove it.

One of the most explosive Snowden revelations exposed a then-secret technique known as "about" surveillance. As the New York Times first reported, the NSA "is searching the contents of vast amounts of Americans' e-mail and text communications into and out of the country, hunting for people who mention information about foreigners under surveillance." In other words, the NSA doesn't just target a contact overseas – it sweeps up everyone's international communications into a dragnet and searches them for keywords.

The Snowden leaks also pushed the Justice Department to admit – contrary to what it told the court – that the government hadn't been notifying any defendants they were being charged based on NSA surveillance, making it actually impossible for anyone to prove they had standing to challenge the Fisa Amendments Act as unconstitutional.

It's unclear how much Solicitor General Donald Verrilli knew when he told the government's lies – twice – to the justices of the supreme court. Reports suggest that he was livid when he found out that his national security staff at the Justice Department misled him about whether they were notifying defendants in criminal trials of surveillance. And we don't know if he knew about the "about" surveillance that might well have given the ACLU standing in the case. But we do know other Justice Department officials knew about both things, and they have let both lies stand without correcting the record.

Read More

NSA Using Same Tactics As Knucklehead Online Scammers — Using Fake Facebook Sites To Infect Computers With Surveillance Software

NSA Geek-Ghouls Attacking All Computers in Every Possible Way
NSA Geek-Ghouls Attacking All Computers in Every Possible Way.
(Photo by hj barraza)

The National Security Agency has reportedly used automated systems to infect user computers with malware since 2010, according to a Wednesday report. And at times the agency pretended to be Facebook to install its malware.

The NSA has been using a program codenamed TURBINE to contaminate computers and networks with malware "implants" capable of spying on users, according to the Intercept, which cited documents provided by whistleblower Edward Snowden.

Between 85,000 and 100,000 of these implants have been deployed worldwide thus far, the report said.

To infect computers with malware, the NSA has relied on various tactics, including posing as Facebook.

Read More

Obama Goes To War Against Another Whistleblower: TSA Whistleblower Tried To Bring Concerns To Superiors — Came Under Attack


TSA Whistleblower Air Marshal Robert MacLean.
(Screen capture from YouTube video)

By Peter Van Buren
The Obama administration has just opened a new front in its ongoing war on whistleblowers. It’s taking its case against one man, former Transportation Security Administration (TSA) Air Marshal Robert MacLean, all the way to the Supreme Court. So hold on, because we’re going back down the rabbit hole with the Most Transparent Administration ever.

Despite all the talk by Washington insiders about how whistleblowers like Edward Snowden should work through the system rather than bring their concerns directly into the public sphere, MacLean is living proof of the hell of trying to do so. Through the Supreme Court, the Department of Justice (DOJ) wants to use MacLean’s case to further limit what kinds of information can qualify for statutory whistleblowing protections. If the DOJ gets its way, only information that the government thinks is appropriate — a contradiction in terms when it comes to whistleblowing — could be revealed. Such a restriction would gut the legal protections of the Whistleblower Protection Act and have a chilling effect on future acts of conscience.

Having lost its case against MacLean in the lower courts, the DOJ is seeking to win in front of the Supreme Court. If heard by the Supremes — and there’s no guarantee of that — this would represent that body’s first federal whistleblower case of the post-9/11 era. And if it were to rule for the government, even more information about an out-of-control executive branch will disappear under the dark umbrella of “national security.”

Read More

Related video:
NSA Whistleblower Thomas Drake speaks at National Press Club


Diagonal Mass Surveillance: If You're Targeted, the Government Can Legally Collect Information On You, Your Friends, and Friends of Your Friends


Filipino protesters join global protest against mass surveillance, (February 2014/ Demotix/Ezra Acayan/All rights reserved)
Filipino protesters join global protest against mass surveillance, (February 2014/
Demotix/Ezra Acayan/All rights reserved)
By Didier Bigo
Mass surveillance does not follow the vertical logic of pure state surveillance as imagined by Orwell. Rather, it is diagonal – building on the information we voluntarily disclose to engage in our own "surveillance" of online friends. This makes it much more perverse.

In the wake of disclosures by Edward Snowden about the NSA practices concerning PRISM and other US surveillance programmes like Xkeyscore, Upstream, Quantuminsert, Bullrun, Dishfire, and the close involvement in these activities of services like the GCHQ (Tempora program), there is an urgent need for a systematic assessment of the scale, reach and character of contemporary surveillance practices, as well as of the justifications they attract and the controversies they provoke.

The public needs to know whether these practices mark a significant reconfiguration of, say, relations between intelligence gathering and surveillance of the Internet and other systems of telecommunications, or mark sustained challenges to fundamental rights in the digital sphere.

There is also a need to pay close attention to the longer-term implications of practices that have already raised serious questions about the widespread transgression of legal principles and democratic norms. And finally, to how transnational surveillance resonates with contemporary shifts in the locus and character of sovereign authority and political legitimacy.

Revelations about practices of large scale surveillance that branch out into the surveillance of everyday activities and bulk intelligence gathering on big groups of people has rightly generated considerable controversy. Yet, there is a danger that both the popular and scholarly debates will be reduced to familiar narratives about technological developments reshaping relations between the watcher and the watched, or the fulfilment of predictions by Georges Orwell or Philip K. Dick, or the transformation of representative democracies into totalitarian regimes in the name of protection.

No – what we see here is not a horizontal system of surveillance (a rhyzome), where surveillance is pervasive but not centralised, and in which we participate because we individually want to take advantage of surveillance (for example by seeing what our friends do on Facebook), or that we enact through voluntary disclosure of information to online friends. Nor does this system follow the vertical logic of pure state surveillance imagined by Orwell in his novel 1984 (a total surveillance).

The diagonal of the bishop: surveillance and intelligence in a transnational world

The current situation could be best conceptualised as a tri-dimensional chess bishop, a "diagonalised" form of surveillance and intelligence. The meaning of the acronym PRISM is revealing in this regard: Planning Tool for Resource Integration, Synchronisation and Management. This long range, diagonalised form transforms the horizontal network of everyday surveillance (e.g. our individual and voluntary use of social media) into the vertical emergence of relevant information.

This selection from bulk of what information is relevant and needs to be investigated is an automated process, regulated by complex algorithms and the use of specific keywords. There is thus a double movement, from the inside out and the outside in, where personal information is voluntarily shared but then secretly recaptured by intelligence agencies. The watched, therefore, participate in their own surveillance.

The fact that these practices ignore national borders and treat information in bulk raises a series of questions. Of these, two are central. The first one concerns the conceptual disconnect between the idea of an interstate world in which each state has a clear vision of its own national security and the practices brought forward by global surveillance. Current surveillance practices involve a network of different intelligence services (the so-called Five Eyes plus) sharing some information in the name of global antiterrorism while also acting against their partners in the pursuit of their own national security interests, thereby destabilising traditional understandings of alliances and state behavior.

The second consequence concerns the strategies deployed by multiple actors to resist surveillance practices, through diplomatic or legal means, as well as adjustments in everyday online behaviour by Internet users. A crucial question is thereby posed: will these users continue to participate in their own surveillance through self-exposure, or will they develop new forms of subjectivity that give more thought to the consequences of their own actions?

Intelligence work begins as analysts use the data collected through large scale surveillance with the goal of identifying unknown persons related to a targeted individual or group, within three degrees of separation ("hops"). For example, if a suspected individual has 100 Facebook friends, the person in charge of the surveillance at the NSA or one of its private subcontractors can without warrant follow the communications of friends of friends of friends, for up to three hops – about 2,669,556 people.

Faced by the magnitude of data accumulated, the strategy used by the analysts is not to read all the content of these communications, but to visualise the graph of interpersonal relations ("meta-data") hoping to disconnect specific connection nodes. This is far from a full reading of everything the data contains, but also equally far from a scientific method that would give a required level of certainty and any semblance of truth to the results.

This method is essentially suspicion elevated to the rank of art. It depends on the analyst's intuition and interpretation, and the results may be contradictory from one analyst to the other. The fear of an omniscient big brother is mostly irrelevant in this scenario, as the claim of any truth coming from this visualisation must be a false one, based as it is upon the pretence that predictions can be elaborated regarding specific human actions at some point in the future, when even general forecasts about trends are difficult. Technology is used as if it could provide scientific certainty about the future, but this belief in the power of 'big data' has more to do with blind faith than with any kind of certainty.

Artist Kaya Mar portrays Barack Obama spying on a blindfolded USA, July 2013/ Demotix/Pete Riches/All rights reserved.
Artist Kaya Mar portrays Barack Obama spying on a blindfolded USA, July 2013/
Demotix/Pete Riches/All rights reserved.


National security and the digitisation of the raison d'etat

These ways to gather and share information have paradoxical effects on national security requirements. Namely, national security is not national any more: different national security imperatives may clash between allies and trust is eroded. The digitisation of national security creates big data gathered at a transnational scale, blurring the lines of what is national as well as the boundaries between law enforcement and intelligence.

These methods encourage a move from the judicial framework of criminal police to preventive, pre-emptive, predictive approaches, and from a high degree of certainty about a small amount of data to a high degree of uncertainty about a large amount of data. The hybridisation of public agencies and private contractors destabilises the process of socialisation via national state interests and thus secrecy, opening up the potential for major leaks by persons holding incompatible values (as in Snowden's case).

To say this more theoretically, the change and uncertainty surrounding the categories of “foreign” and “domestic” is dispersing them through the webs of multiple interconnections. This transforms the line that clearly separated the foreign and the domestic into a Möbius strip. By projecting national security inside out, via a transnational, public-private alliance of national security and sensitive data professionals, an unexpected outside comes into effect whereby every Internet user is targeted. These “data subjects” must react in turn, if they do not accept a situation where nearly all internet users are treated as potential suspects and on principle, not innocent.

Multiple sites of resistance

In this regard, the Snowden revelations set off a snowball effect of distrust among the actors who initially thought that they were gaining from exchanging data with the NSA. The recent partners of the Five Eyes plus (Sweden, Germany, France) felt betrayed when the NSA and GCHQ publicly defended their actions by asking something along the lines of, "You knew that we were spying on you all and your heads of state. Were you so naïve as not to have imagined what we were doing ?".

The same argument has been used to confront the broader public and internet actors, some of whom (such as Google, Yahoo or Facebook) denied all knowledge of the extent of these surveillance practices. The NSA and GCHQ argued that their practices were not the problem, but rather our collective naivety in trusting them, when obviously we did not have to.

This trick may save them from juridical claims by forcing courts to consider that internet users did not have a reasonable expectation of privacy when they sent their emails. Yet, by indirectly acknowledging that they are not to be trusted, they have destabilised their own system of legitimisation. For example, the Snowden revelations have pushed private telecom providers such as the French company Orange into inspecting their technical infrastructures (notably the submarine cables that link Europe to North Africa or Asia), in order to discover that the NSA had abused their initial, more legitimately motivated collaboration (fighting against terrorism and organised crime) by secretly installing backdoors to intercept communications going through the main nodes in France, Germany, Sweden, the Netherlands and possibly Brazil.

The politicians of the Five Eyes plus countries are now caught between their official support for fighting terrorism by all means, Americanophilia, the arguments for a common alliance, and the aggressive behaviour of the Five Eyes network. If most of them consider that they have succeeded in silencing resentment from within the state apparatus (investigative magistrates or prosecutors for example, who are theoretically the 'end users' of gathered intelligence), they have not so far managed to do the same with the private providers and even less with civil society.

Hundreds of judicial claims coming from very different groups – internet actors, telecom providers, NGOs, political parties and citizen movements - have been launched with very different motives in each case, and it will be impossible to accommodate them without engaging in profound reform. The NSA - a Gulliver who wanted to know everything about everyone - has just managed to mobilise all the Lilliputians and might soon be paralysed by their minuscule but solid nets.

This short intervention is part of a longer collective article co-written by Zygmunt Bauman, Didier Bigo, Paulo Esteves, Elspeth Guild, Vivienne Jabri, David Lyon, Rob Walker.

[1] Barack Obama, following one of the 45 recommendations of the review group on intelligence and communication technology delivered on 12 Dec 2013, seems ready to restrict the search without warrant to two "hops" (i.e. 16,340 people), while keeping the principle alive.


Reprinted with permission from openDemocracy.

Glenn Greenwald Was Very Suspiscious Of News Outlets Funded By The Rich — 7 Years Ago

Left: Glenn Greenwald (then of Salon) debates Ben Smith (then of Politico) over  Politico's funding by rich right-wingers, back in May of 2007
Left: Glenn Greenwald (then of Salon) debates Ben Smith (then of Politico) over
Politico's funding by rich right-wingers, back in May of 2007. (Screen capture from
video).
Back in May of 2007 Glenn Greenwald was raising serious questions about what he considered to be Politico's "right-wing bias."

RELATED STORY:
Glenn Greenwald's Billionaire Benefactor Helped Fund 'Regime Change' in Ukraine: Summary of Greenwald's Response — So What?

Greenwald argued this bias was related to
Politico being financed and managed by rich right-wingers, including a CEO who was closely associated with Ronald Reagan.
Greenwald claimed that the writings of journalists are influenced by what they believe are the political views of rich owners.

Greenwald's views have changed a lot since then.


Voyuerism Within NSA Exposed: Webcam Images of Millions of Yahoo Users Intercepted by US & British Spy Agencies

"The original webcam shot". (Photo by Gisela Giardino)

UK, US spies 'stored millions of Yahoo webcam images': report (via AFP)
Britain's communications spy agency GCHQ and the US National Security Agency (NSA) intercepted and stored images from webcams used by millions of Yahoo users, the Guardian newspaper reported on Thursday. GCHQ files leaked by former NSA contractor Edward…

The DEA Is Using Info Illegally Obtained By The NSA To Illegally Prosecute Americans - An Online DEA Manual Shows Cops How To Lie About It


EFF NSA logo parody. (By Electronic_Frontier_Foundation)

By
Whoever suggests the Snowden revelations mean nothing to the lives of ordinary black people either isn't paying close attention, or is working for the police and prison state. The federal DEA, the Justice Department's federal drug police, have passed tons illegal NSA spying data to local police agencies and cynically coached them to lie about the sources of their evidence. It's not exaggeration or hype. You can view the manuals online for yourself.

One of the least remarked upon chunks of Edward Snowden's voluminous revelations about government spying on civilians has been the fact that the Drug Enforcement Administration, the federal police agency created to fight the war on drugs, has funneled illegal NSA surveillance to local police agencies around the country.

New disclosures now allow us to see online the DEA training manuals with which Drug Enforcement Administration agents are taught to coach local police departments across the country how to lie about their chains of evidence and sources, how to willfully violate the law and cover their tracks  in thousands or tens of thousands of cases every year in order to fill the cells of the US prison state with drug defendants.

Continue Reading...

The Wild West of Surveillance Explained: Selling Your Secrets, Building Backdoors, Bounty Hunters, Harvesting Your Data - Which Way Out?

"Spy Tech"
"Spy Tech" (Photo by Peter Terrone)
Here we have an anatomy of a surveillance world that grows more, not less, powerful and full of itself with every passing moment and technological advance, a national security world whose global ambitions know no bounds.


By Pratap Chatterjee and Tom Engelhardt
The question Senator Ron Wyden asked on March 12 of last year was straightforward enough and no surprise for Director of National Intelligence James Clapper. He had been given it a day in advance of his testimony before the Senate Intelligence Committee and after he was done, Senator Wyden and his staff offered him a chance to “amend” his answer if he wished. Did the National Security Agency, Wyden wanted to know, gather “any type of data at all on millions or hundreds of millions of Americans”? Being on that committee and privy to a certain amount of secret intelligence information, Wyden already knew the correct answer to the question. Clapper, with a day to prepare, nonetheless answered, “No, sir. Not wittingly. There are cases where they could inadvertently perhaps collect, but not wittingly.”

That was a bald-faced lie, though Clapper would later term it the “least untruthful” thing he felt he could say. As we now know, the NSA was, among many other things, gathering the phone “data” of every American and storing it for future use. In other words, after some forethought, the director perjured himself.

Mind you, Clapper isn’t exactly shy about charging other people with implicit crimes. In recent testimony before Congress, he demanded that whistleblower and former NSA contractor Edward Snowden “and his accomplices” return all agency documents. It was a stunning use of a term whose only meaning is criminal and clearly referred to the journalists - Glenn Greenwald, filmmaker Laura Poitras, and reporters from the Guardian, the New York Times, and the Washington Post, among other papers - who have been examining and writing about the Snowden documents.

It caught something of the chutzpah of the top officials who run Washington’s national security state - and little wonder that they feel emboldened and demanding. After all, not only is Clapper not going to be charged with perjury, but he has retained his post without a blink. He has kept the “support” of President Obama, who recently told CNN’s Jake Tapper (in what passes these days for a rebuke of our surveiller-in-chief), “Jim Clapper himself would acknowledge, and has acknowledged, that he should have been more careful about how he responded.” More careful indeed!

I've long argued that while we, the citizens of the US, remain in legal America, the US national security state exists in "post-legal America" because no illegal act from warrantless surveillance to torture committed in its service will ever be prosecuted. So it's no surprise that Clapper won’t even be forced to resign for lying to Congress. He's free as a bird and remains powerful indeed. Tell that to some of our whistleblowers.

In his latest post, TomDispatch regular Pratap Chatterjee offers an anatomy of a surveillance world that grows more, not less, powerful and full of itself with every passing moment and technological advance, a national security world whose global ambitions know no bounds. Tom Engelhardt

Selling your secrets
By Pratap Chatterjee
Imagine that you could wander unseen through a city, sneaking into houses and offices of your choosing at any time, day or night. Imagine that, once inside, you could observe everything happening, unnoticed by others - from the combinations used to secure bank safes to the clandestine rendezvous of lovers. Imagine also that you have the ability to silently record everybody’s actions, whether they are at work or play without leaving a trace. Such omniscience could, of course, make you rich, but perhaps more important, it could make you very powerful.

That scenario out of some futuristic sci-fi novel is, in fact, almost reality right now. After all, globalization and the internet have connected all our lives in a single, seamless virtual city where everything is accessible at the tap of a finger. We store our money in online vaults; we conduct most of our conversations and often get from place to place with the help of our mobile devices. Almost everything that we do in the digital realm is recorded and lives on forever in a computer memory that, with the right software and the correct passwords, can be accessed by others, whether you want them to or not.

Now - one more moment of imagining - what if every one of your transactions in that world was infiltrated? What if the government had paid developers to put trapdoors and secret passages into the structures that are being built in this new digital world to connect all of us all the time? What if they had locksmiths on call to help create master keys for all the rooms? And what if they could pay bounty hunters to stalk us and build profiles of our lives and secrets to use against us?

Well, check your imagination at the door, because this is indeed the brave new dystopian world that the US government is building, according to the latest revelations from the treasure trove of documents released by National Security Agency whistleblower Edward Snowden.

Over the last eight months, journalists have dug deep into these documents to reveal that the world of NSA mass surveillance involves close partnerships with a series of companies most of us have never heard of that design or probe the software we all take for granted to help keep our digital lives humming along.

There are three broad ways that these software companies collaborate with the state: a National Security Agency program called “Bullrun” through which that agency is alleged to pay off developers like RSA, a software security firm, to build “backdoors” into our computers; the use of “bounty hunters” like Endgame and Vupen that find exploitable flaws in existing software like Microsoft Office and our smartphones; and finally the use of data brokers like Millennial Media to harvest personal data on everybody on the internet, especially when they go shopping or play games like Angry Birds, Farmville, or Call of Duty.

Of course, that’s just a start when it comes to enumerating the ways the government is trying to watch us all, as I explained in a previous TomDispatch piece, “Big Bro is Watching You.” For example, the FBI uses hackers to break into individual computers and turn on computer cameras and microphones, while the NSA collects bulk cell phone records and tries to harvest all the data traveling over fiber-optic cables. In December 2013, computer researcher and hacker Jacob Appelbaum revealed that the NSA has also built hardware with names like Bulldozer, Cottonmouth, Firewalk, Howlermonkey, and Godsurge that can be inserted into computers to transmit data to US spooks even when they are not connected to the internet.

“Today, [the NSA is] conducting instant, total invasion of privacy with limited effort,” Paul Kocher, the chief scientist of Cryptography Research, Inc. which designs security systems, told the New York Times. “This is the golden age of spying.”

Building backdoors
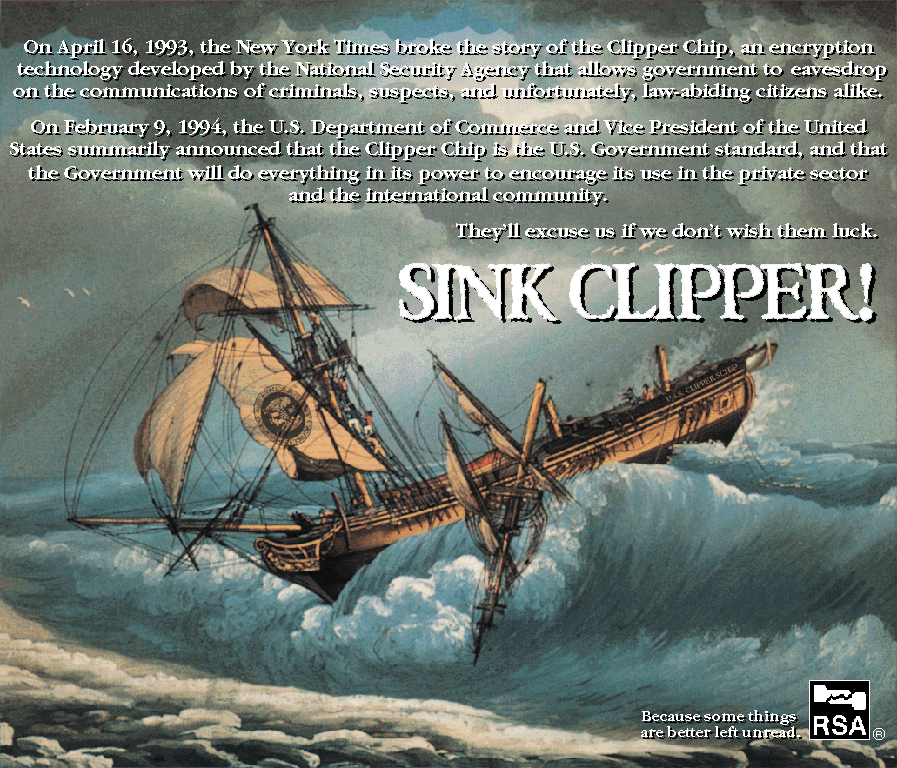
Back in the 1990s, the Clinton administration promoted a special piece of NSA-designed hardware that it wanted installed in computers and telecommunication devices. Called the Clipper Chip, it was intended to help scramble data to protect it from unauthorized access - but with a twist. It also transmitted a "Law Enforcement Access Field" signal with a key that the government could use if it wanted to access the same data.

Activists and even software companies fought against the Clipper Chip in a series of political skirmishes that are often referred to as the Crypto Wars. One of the most active companies was RSA from California. It even printed posters with a call to “Sink Clipper.” By 1995, the proposal was dead in the water, defeated with the help of such unlikely allies as broadcaster Rush Limbaugh and Senators John Ashcroft and John Kerry.

But the NSA proved more tenacious than its opponents imagined. It never gave up on the idea of embedding secret decryption keys inside computer hardware - a point Snowden has emphasized (with the documents to prove it).

A decade after the Crypto Wars, RSA, now a subsidiary of EMC, a Massachusetts company, had changed sides. According to an investigative report by Joseph Menn of Reuters, it allegedly took $10 million from the National Security Agency in exchange for embedding an NSA-designed mathematical formula called the Dual Elliptic Curve Deterministic Random Bit Generator inside its Bsafe software products as the default encryption method.

The Dual Elliptic Curve has a “flaw” that allows it to be hacked, as even RSA now admits. Unfortunately for the rest of us, Bsafe is built into a number of popular personal computer products and most people would have no way of figuring out how to turn it off.

According to the Snowden documents, the RSA deal was just one of several struck under the NSA’s Bullrun program that has cost taxpayers over $800 million to date and opened every computer and mobile user around the world to the prying eyes of the surveillance state.

“The deeply pernicious nature of this campaign - undermining national standards and sabotaging hardware and software - as well as the amount of overt private sector cooperation are both shocking,” wrote Dan Auerbach and Kurt Opsahl of the Electronic Frontier Foundation, a San Francisco-based activist group that has led the fight against government surveillance. “Back doors fundamentally undermine everybody's security, not just that of bad guys.”


Bounty hunters
For the bargain basement price of $5,000, hackers offered for sale a software flaw in Adobe Acrobat that allows you to take over the computer of any unsuspecting victim who downloads a document from you. At the opposite end of the price range, Endgame Systems of Atlanta, Georgia, offered for sale a package named Maui for $2.5 million that can attack targets all over the world based on flaws discovered in the computer software that they use. For example, some years ago, Endgame offered for sale targets in Russia including an oil refinery in Achinsk, the National Reserve Bank, and the Novovoronezh nuclear power plant. (The list was revealed by Anonymous, the online network of activist hackers.)

While such “products,” known in hacker circles as “zero day exploits,” may sound like sales pitches from the sorts of crooks any government would want to put behind bars, the hackers and companies who make it their job to discover flaws in popular software are, in fact, courted assiduously by spy agencies like the NSA who want to use them in cyberwarfare against potential enemies.

Take Vupen, a French company that offers a regularly updated catalogue of global computer vulnerabilities for an annual subscription of $100,000. If you see something that you like, you pay extra to get the details that would allow you to hack into it. A Vupen brochure released by Wikileaks in 2011 assured potential clients that the company aims “to deliver exclusive exploit codes for undisclosed vulnerabilities” for “covertly attacking and gaining access to remote computer systems.”

At a Google sponsored event in Vancouver in 2012, Vupen hackers demonstrated that they could hijack a computer via Google’s Chrome web browser. But they refused to hand over details to the company, mocking Google publicly. “We wouldn’t share this with Google for even $1 million,” Chaouki Bekrar of Vupen boasted to Forbes magazine. “We don’t want to give them any knowledge that can help them in fixing this exploit or other similar exploits. We want to keep this for our customers.”

In addition to Endgame and Vupen, other players in this field include Exodus Intelligence in Texas, Netragard in Massachussetts, and ReVuln in Malta.

Their best customer? The NSA, which spent at least $25 million in 2013 buying up dozens of such “exploits.” In December, Appelbaum and his colleagues reported in Der Spiegel that agency staff crowed about their ability to penetrate any computer running Windows at the moment that machine sends messages to Microsoft. So, for example, when your computer crashes and helpfully offers to report the problem to the company, clicking yes could open you up for attack.

The federal government is already alleged to have used such exploits (including one in Microsoft Windows) - most famously when the Stuxnet virus was deployed to destroy Iran’s nuclear centrifuges.

“This is the militarization of the Internet,” Appelbaum told the Chaos Computer Congress in Hamburg. “This strategy is undermining the internet in a direct attempt to keep it insecure. We are under a kind of martial law.”

Harvesting your data
Among the Snowden documents was a 20-page 2012 report from the Government Communications Headquarters (GCHQ) - the British equivalent of the NSA - that listed a Baltimore-based ad company, Millennial Media. According to the spy agency, it can provide “intrusive” profiles of users of smartphone applications and games. The New York Times has noted that the company offers data like whether individuals are single, married, divorced, engaged, or “swinger,” as well as their sexual orientation (“straight, gay, bisexuall, and ‘not sure’”).

How does Millennial Media get this data? Simple. It happens to gather data from some of the most popular video game manufacturers in the world. That includes Activision in California which makes Call of Duty, a military war game that has sold over 100 million copies; Rovio of Finland, which has given away 1.7 billion copies of a game called Angry Birds that allows users to fire birds from a catapult at laughing pigs; and Zynga - also from California - which makes Farmville, a farming game with 240 million active monthly users.

In other words, we’re talking about what is undoubtedly a significant percentage of the connected world unknowingly handing over personal data, including their location and search interests, when they download “free” apps after clicking on a licensing agreement that legally allows the manufacturer to capture and resell their personal information. Few bother to read the fine print or think twice about the actual purpose of the agreement.

The apps pay for themselves via a new business model called “real-time bidding” in which advertisers like Target and Walmart send you coupons and special offers for whatever branch of their store is closest to you. They do this by analyzing the personal data sent to them by the “free” apps to discover both where you are and what you might be in the market for.

When, for instance, you walk into a mall, your phone broadcasts your location and within a millisecond a data broker sets up a virtual auction to sell your data to the highest bidder. This rich and detailed data stream allows advertisers to tailor their ads to each individual customer. As a result, based on their personal histories, two people walking hand in hand down a street might get very different advertisements, even if they live in the same house.

This also has immense value to any organization that can match up the data from a device with an actual name and identity - such as the federal government. Indeed, the Guardian has highlighted an NSA document from 2010 in which the agency boasts that it can “collect almost every key detail of a user's life: including home country, current location (through geolocation), age, gender, zip code, marital status… income, ethnicity, sexual orientation, education level, and number of children.”

In denial
It’s increasingly clear that the online world is, for both government surveillance types and corporate sellers, a new Wild West where anything goes. This is especially true when it comes to spying on you and gathering every imaginable version of your “data.”

Software companies, for their part, have denied helping the NSA and reacted with anger to the Snowden disclosures. “Our fans’ trust is the most important thing for us and we take privacy extremely seriously,” commented Mikael Hed, CEO of Rovio Entertainment, in a public statement. “We do not collaborate, collude, or share data with spy agencies anywhere in the world.”

RSA has tried to deny that there are any flaws in its products. "We have never entered into any contract or engaged in any project with the intention of weakening RSA’s products, or introducing potential ‘backdoors’ into our products for anyone’s use,” the company said in a statement on its website. “We categorically deny this allegation." (Nonetheless RSA has recently started advising clients to stop using the Dual Elliptical Curve.)

Other vendors like Endgame and Millennial Media have maintained a stoic silence. Vupen is one of the few that boasts about its ability to uncover software vulnerabilities.

And the NSA has issued a Pravda-like statement that neither confirms nor denies the revelations. "The communications of people who are not valid foreign intelligence targets are not of interest to the National Security Agency," an NSA spokeswoman told the Guardian. "Any implication that NSA's foreign intelligence collection is focused on the smartphone or social media communications of everyday Americans is not true.”

The NSA has not, however, denied the existence of its Office of Tailored Access Operations (TAO), which Der Spiegel describes as “a squad of [high-tech] plumbers that can be called in when normal access to a target is blocked.”

The Snowden documents indicate that TAO has a sophisticated set of tools at its disposal - that the NSA calls “Quantum Theory” - made up of backdoors and bugs that allow its software engineers to plant spy software on a target computer. One powerful and hard to detect example of this is TAO’s ability to be notified when a target’s computer visits certain websites like LinkedIn and to redirect it to an NSA server named “Foxacid” where the agency can upload spy software in a fraction of a second.

Which way out of the walled garden?
The simple truth of the matter is that most individuals are easy targets for both the government and corporations. They either pay for software products like Pages and Office from well known manufacturers like Apple and Microsoft or download them for free from game companies like Activision, Rovio, and Zynga for use inside “reputable” mobile devices like Blackberries and iPhones.

These manufacturers jealously guard access to the software that they make available, saying that they need to have quality control. Some go even further with what is known as the “walled garden” approach, only allowing pre-approved programs on their devices. Apple’s iTunes, Amazon’s Kindle, and Nintendo’s Wii are examples of this.

But as the Snowden revelations have helped make clear, such devices and software are vulnerable both to manufacturer’s mistakes, which open exploitable backdoors into their products, and to secret deals with the NSA.

So in a world where, increasingly, nothing is private, nothing is simply yours, what is an internet user to do? As a start, there is an alternative to most major software programs for word processing, spreadsheets, and layout and design - the use of free and open source software like Linux and Open Office, where the underlying code is freely available to be examined for hacks and flaws. (Think of it this way: if the NSA cut a deal with Apple to copy everything on your iPhone, you would never know. If you bought an open-source phone - not an easy thing to do - that sort of thing would be quickly spotted.) You can also use encrypted browsers like Tor and search engines like Duck Duck Go that don’t store your data.

Next, if you own and use a mobile device on a regular basis, you owe it yourself to turn off as many of the location settings and data-sharing options as you can. And last but hardly least, don’t play Farmville, go out and do the real thing. As for Angry Birds and Call of Duty, honestly, instead of shooting pigs and people, it might be time to think about finding better ways to entertain yourself. Pick up a paintbrush, perhaps? Or join an activist group like the Electronic Frontier Foundation and fight back against Big Brother.

This piece, including Tom Engelhardt's introduction, is reposted from TomDispatch.com with that site's permission.


Reprinted with permission from openDemocracy.

Related Posts Plugin for WordPress, Blogger...